6a, 57 Miller Street Murarrie QLD 4172


In brief
- The Essential Eight is evolving into Essentials for Enterprise IT, with a more flexible, threat-informed approach to cybersecurity.
- Organisations can continue their existing Essential Eight controls, as current security investments are expected to remain relevant.
- Organisations should monitor the new guidance and review contracts, insurance and tenders that specifically reference Essential Eight maturity levels.
Well, it was a nice idea at the time.
When the ASCS first introduced it almost a decade ago, the Essential Eight seemed groundbreaking. It offered eight practical controls to help all companies tighten up their cybersecurity.
However, things have changed. According to the ASD, in 2024-5 only 22% of Commonwealth entities reached Essential Eight Maturity Level 2 or higher across all eight strategies.
These are government agencies with mandated compliance, and it wasn’t even working for them.
That’s why in June 2026, the ASD and ASCS announced that the Essential Eight is going to evolve into a new, broader “Essentials series”. Let’s find out what that means.
What’s actually changing
The current Essential Eight will now make up the first chapter of a multi-chapter series called Essentials for Enterprise IT.
According to ASD, this resource will offer “prioritised, threat-informed mitigations for contemporary technology environments.”
In plain English, that means practical tools and implementation guidance will replace the old, rigid checklist format.
The aim is to give organisations more flexibility when implementing controls while keeping a clear path to resilience.
If you’re already using the Essential Eight, ASD says you can “expect strong alignment with existing controls and investments.”
In a June 2026 interview, an ACSC official said both frameworks will stay live during the transition period, and the Essential Eight will be fully retired in about two years.
What this means for your organisation
As we learned, only a minority of Commonwealth agencies hit their Essential Eight maturity targets.
If resourced agencies with mandated compliance aren’t reaching their goals, these targets were probably never realistic for smaller, resource-constrained private businesses.
In other words, a new model might well be very good news for most organisations. Instead of chasing an unrealistically high score across all eight strategies, you can match controls to your actual exposure and capabilities.
There is something to be aware of, however. If you have any contracts, insurance policies, or tenders that cite a specific or fixed Essential Eight benchmark, you’ll need to figure out your obligations here.
What should you do now?
There’s no need to change anything drastic right now. Mainly, you need to keep doing what’s working and pay attention to the ASD’s announcements.
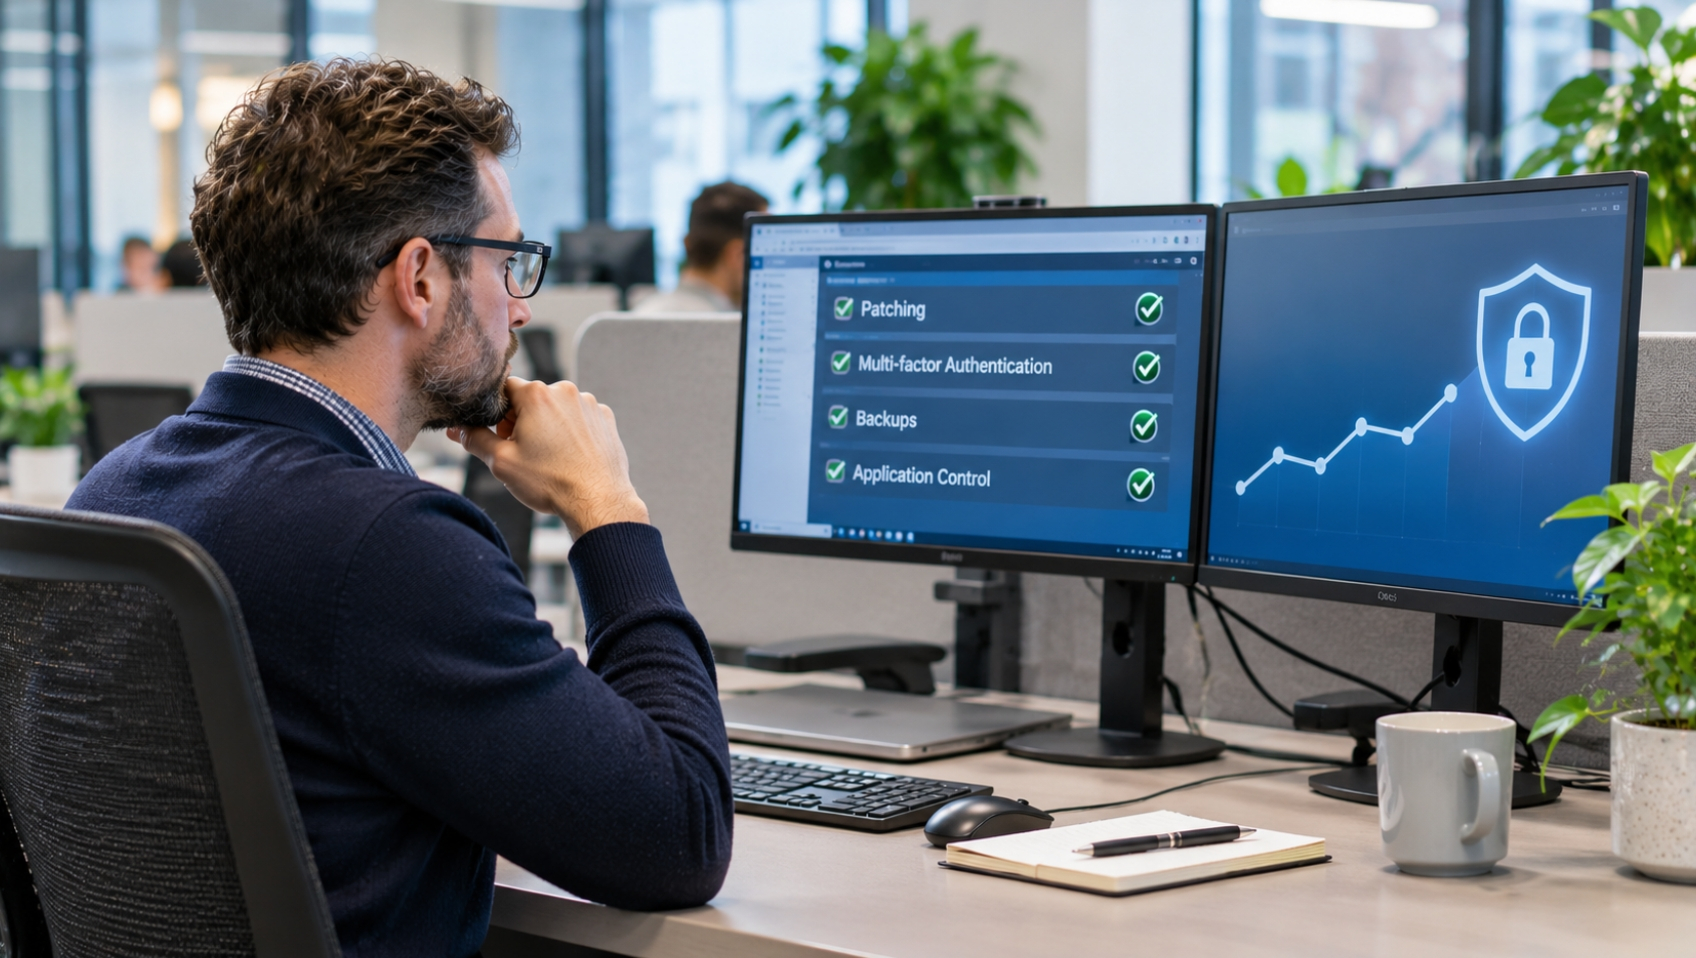
1. Keep your current E8 work going. ASD has said they’ll match the former standards, so any patching, MFA, backups, and application control will carry forward.
2. Watch out for the first published Essentials chapter and review it against your current controls as soon as it lands.
3. Stop defining success as “all eight at ML2.” Instead, prioritise the controls that match your real threat exposure, which is what the new model intends.
4. Audit where “Essential Eight Maturity Level” appears in your obligations. Check contracts, cyber insurance policies and tender responses, because that language will change with the new requirements.
The Essential Eight isn’t really going anywhere. The goals and underpinning philosophy are the same, but it’s been redesigned to make it more useful and easier to comply with.
- June 2026 The ASD and ACSC announced that the Essential Eight would evolve into a broader “Essentials series.”
- During the transition period: Both the existing Essential Eight and the new framework will remain live while organisations transition to the new approach.
- Around 2028 Essential Eight is expected to be fully retired in about two years.
- As the Essentials guidance rolls out: Organisations should monitor ASD announcements and review the first published Essentials chapter against their existing cybersecurity controls once it is released.